
Hackers cook supermarket fridges across Europe, heating them to 50°C
Attackers have tampered with the refrigeration and freezer systems of supermarkets in at least eight European countries and turned up the temperatures. Tons of food had to be thrown away. It's the second wave in three weeks, and the culprit is unknown.
What this is about
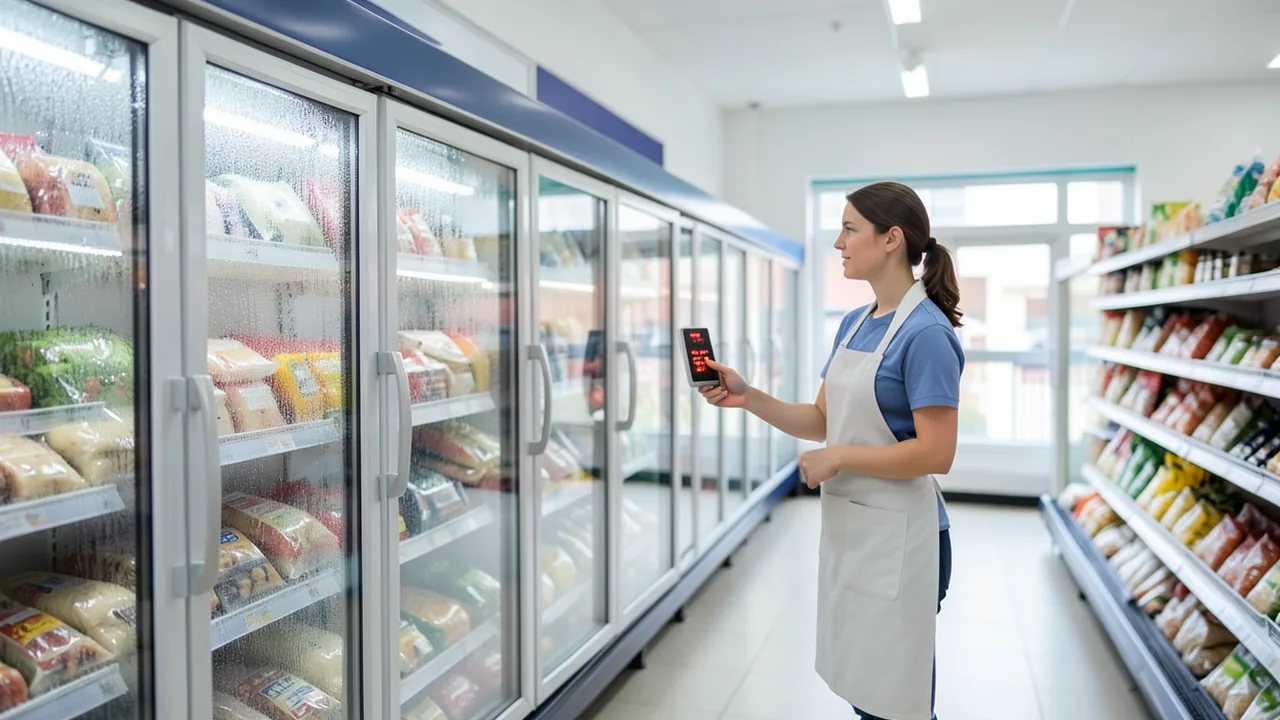
On November 2, 2026, supermarket refrigeration and freezer systems were hacked in several European countries. The attackers raised temperatures remotely, spoiling fresh and frozen food. According to Reuters, stores in eight countries were affected. The sources name Sweden, Belgium, Luxembourg, Ireland, Germany, the Netherlands, Estonia, Finland, Italy and Portugal, among others. The country lists differ from source to source. Reuters describes the attack as identical to one that played out in France three weeks ago.
What happened
According to Taiwan's UDN, citing Reuters, the attack in Sweden began at around 2 a.m. but wasn't noticed until hours later. A sales manager at an ICA store in Stockholm said: "Everything is ruined. All the freezers have risen to 50 degrees." Another source also reports 50°C (122°F) for Estonia, hot enough to speed up bacterial growth dramatically.
Affected companies and locations include:
- Carrefour Belgium: 15 of 700 stores.
- Colruyt: five Spar stores.
- IKEA: at least one store in Belgium.
- Coop Sweden: six to seven stores. ICA: 23 stores, according to Reuters.
- SuperValu Ireland (Musgrave): 13 stores, with goods pulled from sale.
- Delhaize Luxembourg: four stores.
- Edeka: one store in Reisbach, Germany.
- Italy: Radenza Group (Coop stores in Sicily). The freezer sections were attacked at around 4 a.m.
- Portugal: seven Intermarché stores.
Belgian butcher Luc De Laet got a call from his staff at 3:30 a.m. At his shop near Antwerp, the fridges had been set to 18°C, and meat worth around €15,000 was unusable. He filed a complaint. He suspects the attackers wanted to destabilize the European economy.
The backstory in France
The first attack came in October in France. Finance Minister Roland Lescure told parliament on October 13 that about 700 of 10,000 supermarkets had been affected. According to French authorities, the systems were put into a permanent defrost mode, which spoiled food and even started fires in some places. Carrefour alone recorded around 80 affected franchise stores, the Mousquetaires group about 300, and Coopérative U 80 of 2,000 stores. France's CERT-FR identified compromised remote-control modules from Danfoss and Copeland. Euronews gives October 12 as the date and reports that French authorities believed international actors were involved, without officially attributing the attack.
Vulnerabilities and technical background
In August, security firm Claroty published flaws in Danfoss AK-SM 800A controllers, including an authentication bypass (you can get in without the correct password). It found 2,765 of these devices exposed on the internet. Danfoss released an update with firmware R4.3.1. According to the sources, it's unclear which flaws were actually exploited in this wave. An Estonian refrigeration provider said the affected devices were older Danfoss models, as in France. Belgian refrigeration firm Sabcobel reports that the evaporators were switched to defrost mode. Older systems sometimes need structural changes, which cost time and money.
CERT-FR warns that the campaigns are likely to continue. It stresses that leaving outdated devices without updates connected to the internet is very risky. Euronews quotes Pavlina Pavlova of Critical Cyber, who says many controllers are older models without security updates, despite vulnerabilities known since 2025.
Retailers' responses
Coop Sweden says it is moving from 4G connections to 5G and modern modems. That work had already begun after the French incident. The seven affected stores are running again, but their cooling systems are now disconnected from the internet. According to the sources, those hit in Sweden used an external Danfoss control system. ICA said all 23 affected stores operated devices outside the centrally managed network. One ICA retailer was in the middle of overhauling his security systems when the attack hit. Swedish police counted about ten complaints and expect more.
Because many supermarkets are run by independent owners in cooperative structures, systems aren't uniform, Reuters says. Edeka confirmed this for its network. Danfoss advised never making systems directly reachable from the internet. Frank Groenewegen of Deloitte advised retailers to check whether their controllers are vulnerable, whether they're connected to the network, whether the latest updates are installed and whether vendor support is in place. If in doubt, take them off the public network immediately. Disconnecting doesn't fix the root cause, he said, but it does isolate the devices.
In the UK, attackers tried to hit small meat processors, according to NCSC chief Richard Horne, but the impact was minimal. Horne sees this as an early sign of more frequent disruption, because old technology can't keep pace with hackers.
Who is behind it?
No one has claimed responsibility so far, and Reuters can confirm neither the perpetrators nor a link to the French case. There is no ransom demand, which points to sabotage. After the second wave, Marta Rybczynska (Ygreky) considers a state-backed actor more likely, unless only the method was copied. Instructions are easy to find online, she notes. EU Agriculture Commissioner Christophe Hansen spoke of a "deliberate attempt" to disrupt the food supply. The EU agency ENISA stressed the importance of European cooperation. Italy called a crisis meeting on cybersecurity, and prosecutors are investigating in several countries. Belgium's Cybersecurity Centre warns that AI could make it easier for attackers to exploit vulnerabilities. Pavlova says AI lowers the barrier to entry and speeds up finding flaws, while patching remains the bottleneck.
A Bing report also mentions a Pentagon investigation into whether hackers also tampered with refrigeration systems at US military bases. No details are available.
Our take
The case shows how vulnerable everyday connected technology is. Refrigeration controllers are often online so they can be monitored remotely, and they're rarely maintained. The impact is concrete: lost goods, empty shelves and, in France, even fires. The culprits, the motive and the exact vulnerability remain open. Whether the waves are connected is also unconfirmed. The only thing established is that older, internet-reachable controllers are affected, and the recommended immediate step is to disconnect them from the public internet and update them. Note: The KuCoin source is a crypto aggregator and sometimes gives differing details (for example, nine countries instead of eight).
Related videos
Sources
- Google News (TW) udn.com
- Bing News (en-GB) syracuse.com
- yahoo.com yahoo.com
- kucoin.com kucoin.com
- euronews.com euronews.com
- AI Times (KR) aitimes.com
- Techmeme cnbc.com
- Google News (GB) news.google.com
Ask the AI assistant
Questions about this article, installation or background? Our assistant knows this page and runs on our own machine, not in someone else's cloud.
The Assistant is an AI (Gemma 4) and can make mistakes – please check important details against the source. Questions are used only to generate an answer and are deleted after one hour. Please don't enter any personal data.
Comments
What do you think? Already tried it? Write it here, no sign-up needed.
Comments are public. Links aren't allowed, and we delete abusive posts. You can delete your own comment at any time in this browser. Learn more in the Privacy Policy.