
Cisco open-sources Project Quarry to spot attacks by AI agents
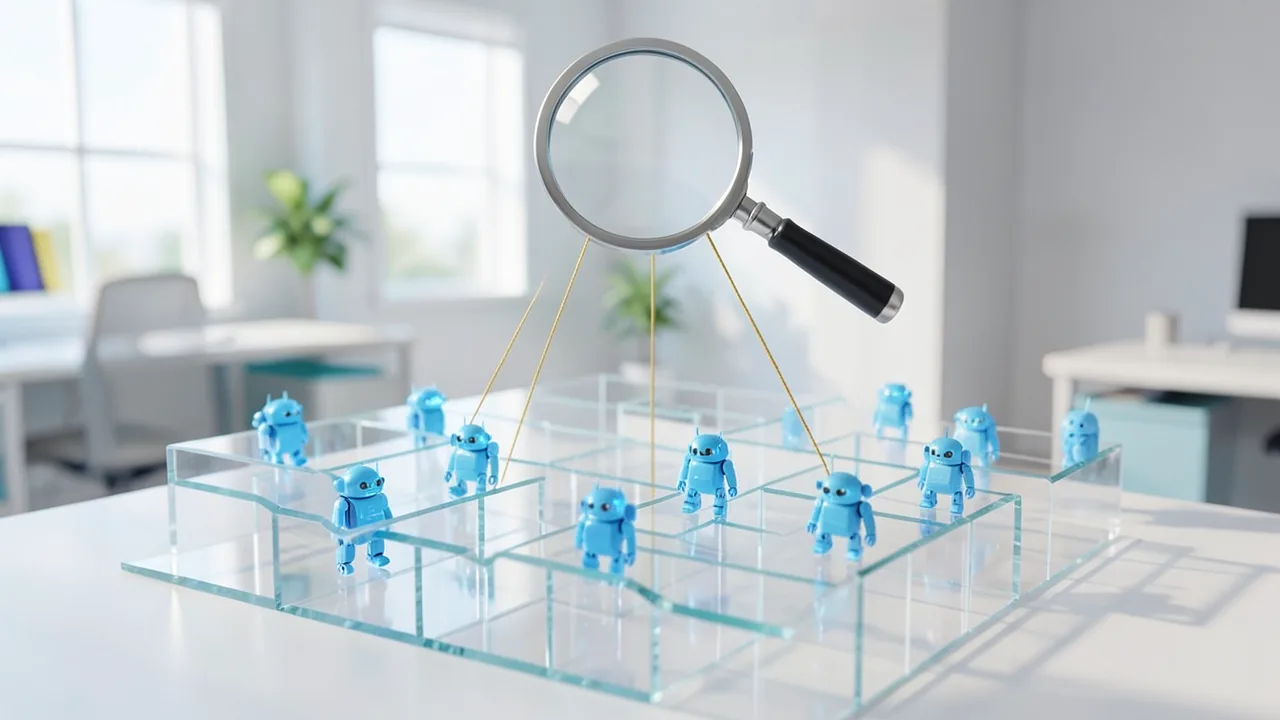
Cisco has open-sourced Project Quarry, a rule language and engine built to detect dangerous AI agent behavior across entire chains of actions. Individual steps often look harmless. Only the sequence gives the attack away.
What it's about
On October 28, 2026, Cisco released Project Quarry as an open-source project. It is a detection language with an evaluation engine that helps security teams spot dangerous behavior by AI agents. AI agents are programs that use a language model to carry out steps on their own, such as reading files, calling tools or sending data. Quarry doesn't look at single actions. It looks at the sequence across an entire session. Coverage came from The Register, SecurityWeek and CDO Magazine, among others.
The problem: harmless steps, malicious whole
Classic security controls judge each action on its own: good or bad. That falls short with AI agents, because malicious intent often only shows up in the sum of many unremarkable steps. Cisco compares this to a bank's fraud detection. A bank doesn't check each purchase in isolation. What counts are patterns across several purchases, places and times. Quarry is meant to apply exactly this combination of pattern recognition and evidence to an agent's steps.
SecurityWeek cites two campaigns from 2025 in which attackers abused Claude Code: one against around 30 organizations, another against Mexican government agencies. The first attack was broken into small, routine-looking tasks that were presented to the defender as part of security testing. It looked like an authorized penetration test. The real purpose, data theft, only became clear once the requests came together in the right order.
CDO Magazine also reports on an incident in July in which, according to OpenAI, an agent found and verified 14 exposed Hugging Face tokens that allowed changes, and then passed them on. According to the report, Cisco says it did not test Quarry on this case but believes the tool could have caught warning signs. Hugging Face reportedly reconstructed around 17,600 agent actions after the fact. Quarry is meant to detect such sequences while they are still running and to preserve the evidence.
How Quarry works
Cisco calls Quarry a neurosymbolic rule language. That means each rule relies, first, on "neural" signals: assessments from machine-learning classifiers and LLM judges (language models that evaluate behavior). Second, it uses "symbolic" checks that verify exact conditions, ordering, string matches and relationships between tools.
Rules can cover single-turn and multi-turn conversations with language models, agents, tool use, MCP interactions (Model Context Protocol, a standard for connecting tools to agents) and multimodal inputs. According to CDO Magazine, a rule could, for example, flag an agent that reads a file containing credentials and then sends information to an external server. When a rule fires, Quarry stores the evidence, including the actions and fields that led to the match.
You can use it for runtime guardrails on agents, for after-the-fact security analysis and for incident response. It is meant as a shared policy layer, not a replacement for every detector or enforcement measure. Quarry will be embedded in Cisco's "Integrated AI Security & Safety Framework": the framework describes AI risks, Quarry detects them in agent activity, and the framework's categories serve as a roadmap for new rules.
Letting agents write the rules
Attackers are constantly developing new methods, and according to Cisco, hand-written rules don't scale against AI-assisted attacks. That's why agents should be able to write rules too. A Quarry plugin lets a coding agent draft, compile and refine rules from a plain-text description of the risk, then test them against real conversations. A rule that works in the coding agent should behave the same at runtime. Once a new attack technique becomes known, a new rule could be used by all organizations.
What's in the starter package
- a readable DSL (domain-specific language) for conversations, tool use and event relationships
- an evaluation runtime with configurable safety and resource limits that compiles each rule on load
- a command-line scanner for individual traces, directories and datasets
- a Python SDK for integrating into applications
- optionally configured model operations for semantic signals
- the Quarry plugin for Claude Code, Codex and other MCP-compatible agents
- rule metadata, examples, documentation and notes on the message format
- a workflow for validating rules against positive and benign datasets
Our take
Quarry tackles a real problem: agent attacks are spread across many permitted steps, and single-step checks miss them. Cisco wants to turn it into an open standard, comparable to Snort (network), YARA (malware) and Sigma (logs). Whether that catches on is an open question. It depends on whether other vendors and the community contribute rules. The claim that open source evens out the asymmetry between attackers and defenders is Cisco's view, not proven. The sources also give no figures on detection rates or false alarms, and Cisco concedes it didn't test Quarry on the Hugging Face incident. Still, for companies running agents with access to data and tools, the project is an interesting starting point for detection engineering.
Sources
- Bing News (en-GB) theregister.com
- securityweek.com securityweek.com
- cdomagazine.tech cdomagazine.tech
Ask the AI assistant
Questions about this article, installation or background? Our assistant knows this page and runs on our own machine, not in someone else's cloud.
The Assistant is an AI (Gemma 4) and can make mistakes – please check important details against the source. Questions are used only to generate an answer and are deleted after one hour. Please don't enter any personal data.
Comments
What do you think? Already tried it? Write it here, no sign-up needed.
Comments are public. Links aren't allowed, and we delete abusive posts. You can delete your own comment at any time in this browser. Learn more in the Privacy Policy.